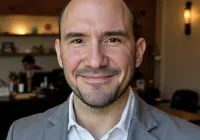
Hey, I'm David O'Neil
I’ve spent more than 20 years in cybersecurity, and most of what I know I learned the hard way: in the middle of an incident, in front of a board, or watching a well-funded program fail for reasons nobody wrote down.
I started hands-on in network and systems security. Since then I’ve run global security operations, built an advisory practice from scratch as a managing director and vCISO, owned the P&L for consulting and managed security services, and now lead security as a CISO for a multi-cloud SaaS company. I’ve worked extortion cases, cloud breaches, insider threats and nation-state intrusions, and I led incident response strategy for the 2018 World Economic Forum in Davos.
I’ve spoken at security conferences and industry groups, including BSides and InfraGard, and I’ve run executive tabletop exercises for leadership teams who wanted to find the gaps before an attacker did. In 2025 I was named an OnCon Top 100 CISO.
CISOExpert is where I do that thinking in public. It’s a knowledge base, not a blog. Some pieces are finished guidance. Others are open questions or experiments, and they say so.
What you’ll find
- Topics - the subjects I work on, from security leadership to operations and AI
- Explore - experiments and research in progress
- Frameworks and Tools - things you can pick up and use
- Articles - the longer write-ups
Every piece shows how mature it is and what would move it forward. How this site works explains the rules, including how I use AI.
Get in touch
Working through a security problem, or think I got something wrong? Tell me. I’d rather be corrected than confident.